Drupal is urging online store owners to patch a highly critical access bypass vulnerability in the Commerce Core module, warning that it is being exploited in the wild. Tracked as CVE-2026-118539, the issue affects a contributed module that adds e-commerce… Read More "Drupal Commerce Core Vulnerability Exploited Against Online Stores "
Cisco SD-WAN Zero-Day Exploitation Tied to Volt Typhoon’s ‘Silent Train’ Network
A threat actor whose infrastructure overlaps with a covert network used by China’s Volt Typhoon exploited a critical Cisco SD-WAN vulnerability to deploy malware designed to harvest encryption keys, Cisco Talos reported on Wednesday. The same day, Lumen’s Black Lotus… Read More "Cisco SD-WAN Zero-Day Exploitation Tied to Volt Typhoon’s ‘Silent Train’ Network"
Chinese Hackers Quietly Used Low-Severity ESXi Logging Flaw as Zero-Day
The US cybersecurity agency CISA on Wednesday warned that hackers have been exploiting another VMware ESXi vulnerability in attacks. Tracked as CVE-2026-41709, the exploited flaw is described as a low-severity insufficient logging issue. It allows attackers logged in as administrators… Read More "Chinese Hackers Quietly Used Low-Severity ESXi Logging Flaw as Zero-Day"
Attackers Exploit Third VeloCloud Orchestrator Zero-Day in Four Months
Networking solutions provider Arista Networks on Thursday rolled out patches for an exploited zero-day vulnerability in its centralized management tool VeloCloud Orchestrator (VCO). The critical-severity security defect is tracked as CVE-2026-114625 (CVSS score of 9.9) and is described as a… Read More "Attackers Exploit Third VeloCloud Orchestrator Zero-Day in Four Months"
Chinese APT Exploited BeyondTrust Vulnerability as Zero-Day
A Chinese APT has been exploiting a BeyondTrust vulnerability as a zero-day since August as part of its state-sponsored espionage operations. The exploited flaw, tracked as CVE-2026-102764 (CVSS score of 9.3), is described as an improper validation of message origins… Read More "Chinese APT Exploited BeyondTrust Vulnerability as Zero-Day"
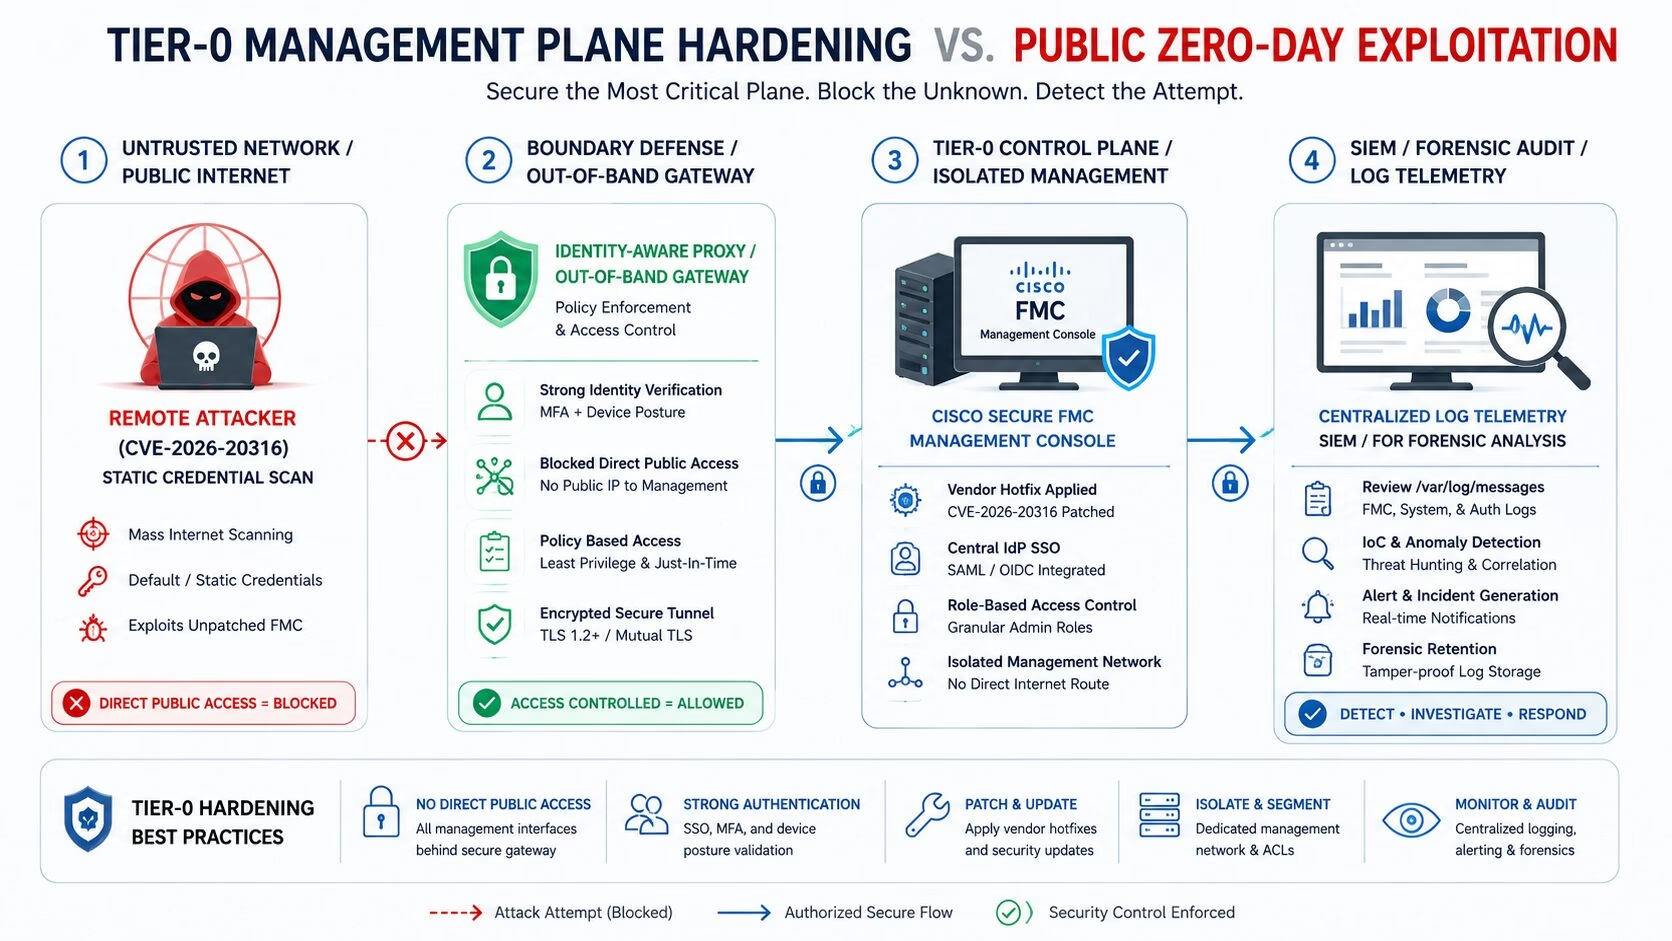
Hardening Tier-0 Management Planes: Lessons from the Cisco Secure FMC Zero-Day (CVE-2026-20316)
Centralized management consoles serve as the nerve center for enterprise network security. When a management plane is compromised, threat actors gain full visibility into firewall configurations, routing tables, and access control policies across the entire corporate infrastructure. The Cybersecurity and… Read More "Hardening Tier-0 Management Planes: Lessons from the Cisco Secure FMC Zero-Day (CVE-2026-20316)"